HackTheBox RoadMap — Phase 7: Capture the Flags
AUTHORCyberAlp0
READ TIME02 MIN
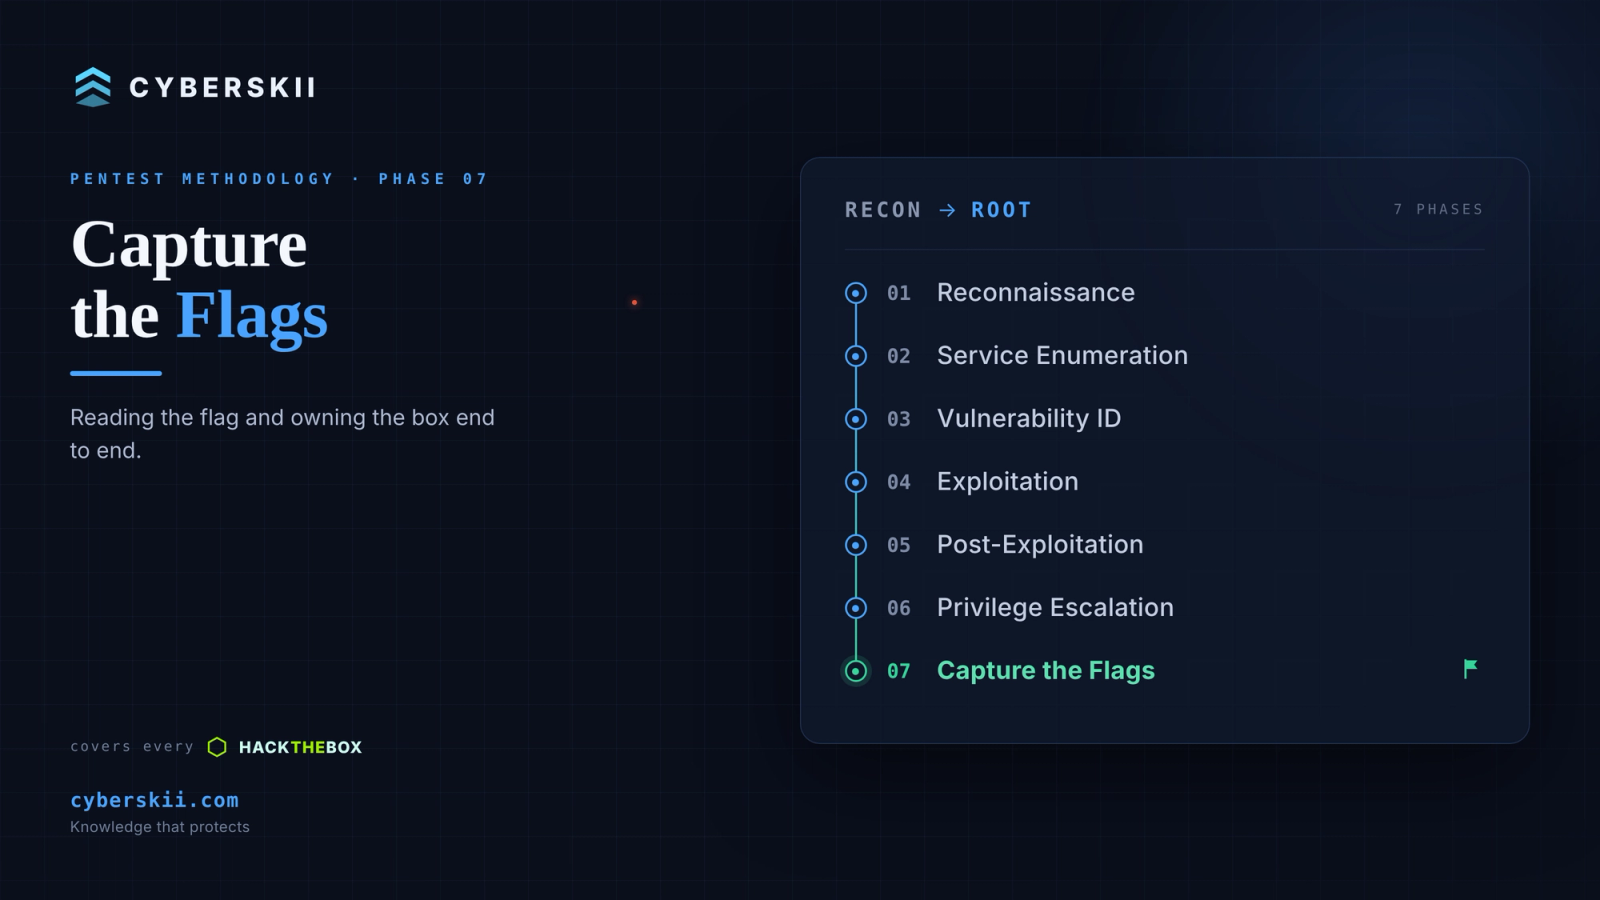
The final phase. After escalating to root / Administrator in Part 6, all that's left is to read the flag and close out the engagement. This article also wraps the whole series with a tools reference and a set of Golden Rules.
Reading the Root Flag
 # Linux
cat /root/root.txt

# Windows
type C:\Users\Administrator\Desktop\root.txt

##If the file's name has spaces, wrap it in quotes
type C:\Users\Administrator\Desktop\"this is the root flag.txt"
Real-world notes
- Sometimes, we never logged in with a password at the end — we logged in with the Administrator's NT hash (extracted from an AD CS certificate for example) using Pass-the-Hash:
impacket-psexec -hashes :<NThash> administrator@<DC_IP>

## then

type C:\Users\Administrator\Desktop\root.txt

##(evil-winrm -i <ip> -u administrator -H <NThash> works too when WinRM is reachable.)- You rarely need the plaintext password — a hash is a valid credential. And remember the operational gotchas that bit us: the HTB IP changes on every reset (re-check
/etc/hostsand your hash if WinRM suddenly times out), and some of the escalation steps were one-shot and irreversible, so get them right before firing. - Let the scan pick the game. The port signature tells you whether you're hunting a web bug or chasing credentials (Part 1).
- Enumerate more than you think you need. Open shares, page source, localhost listeners — the foothold is usually sitting in plain sight (Parts 2 & 5).
- Version strings are gifts. A build number often maps straight to a known CVE (Part 3).
- Abuse features, not just bugs. Management consoles, saved credentials, and trust relationships are the real attack surface (Parts 4 & 6).
- When scanners go quiet, read the raw permissions. The best paths are the ones you build from a narrow right, which (no -vulnerable) flag will ever show you (Parts 3 & 6).
- A hash is a credential. Pass-the-Hash, DPAPI, and certificates all beat cracking (Parts 5–7).
- Mind the clock. Kerberos is time-sensitive (-ntupdate or faketime) saves hours of confusion (Part 6).
That's the full Recon-to-Root in 7 Phases roadmap. Follow it in order on any machine and you'll always know what to do next.